The evolving threat landscape within the non-fungible token (NFT) sector has reached a new level of sophistication, with malicious actors increasingly deploying social engineering tactics to target high-net-worth digital asset collectors. In the latest manifestation of these cyber threats, fraudsters impersonating prominent journalists from esteemed financial publications have attempted to compromise the wallets of Bored Ape Yacht Club (BAYC) holders. The incident highlights the persistent vulnerabilities facing the Web3 ecosystem, where human error often supersedes robust cryptographic security protocols.
The attempt came to light when a prominent BAYC collector known publicly as "Crumz" detailed an elaborate, multi-stage interaction with individuals posing as media personnel from Forbes. The episode underscores a growing trend wherein cybercriminals leverage the allure of mainstream media recognition to lower the guard of unsuspecting cryptocurrency and NFT investors, ultimately attempting to execute unauthorized remote access and asset drainage.
Anatomy of an Impersonation Attack: The Chronology of the Scam
The incident began on the social media platform X (formerly Twitter), where Crumz received a direct message from an individual identifying as Robert Lafranco, purportedly an editor at Forbes. The initial outreach pitched an exclusive feature article focusing on the experiences of early BAYC collectors and their engagement within the broader ecosystem.
Flattered by the prospect of mainstream journalistic coverage, the collector exercised initial caution, performing a cursory digital search that appeared to validate the existence of the purported editor. However, this preliminary verification fell short of detecting the subtle spoofing employed by the fraudsters, who had meticulously constructed a facade of professional credibility. Enticed by the opportunity to discuss the historical and cultural significance of his digital collectibles, Crumz agreed to participate in a recorded interview session via Zoom.
The execution phase of the scam involved deliberate psychological manipulation designed to establish trust and lower suspicions. Initially, the scammers failed to appear for the scheduled video conference, attributing their absence to a fabricated family emergency—a classic social engineering tactic intended to create a sense of obligation and emotional normalization. The meeting was subsequently rescheduled.
When the rescheduled call commenced, multiple red flags immediately surfaced. The participants operating on the side of the supposed media outlet steadfastly refused to activate their webcams, citing persistent technical difficulties. Furthermore, the conversation expanded to include another individual who claimed to be Steven Ehrlich, Forbes’ research director.
Throughout the interview, Crumz recounted his journey within the BAYC community, detailing the utility, community dynamics, and evolution of his digital assets. However, the technical execution of the call revealed glaring operational anomalies. The callers utilized a free tier of Zoom, frequently changing meeting links and exhibiting amateurish operational habits uncharacteristic of major media organizations.

The critical turning point occurred when the individuals requested permission to deploy a separate recording bot to capture the screen session. While the collector initially consented, deep alarm bells rang when the callers issued a bizarre request: they asked Crumz to locate a physical banana and make a vocalization mimicking his Bored Ape character.
Recognizing the absurdity of the request, Crumz excused himself momentarily from the physical space, muting his microphone and turning away from his workstation. During this brief window, the scammers attempted to seize remote control of his computer system. Upon returning, Crumz observed the browser actively navigating to delegate.cash, a legitimate permission-management protocol frequently targeted by exploiters to revoke or reassign token authorities.
Proactive Security Measures Prevent Catastrophic Loss
The potential financial disaster was averted due to the collector’s rigorous security posture. All of Crumz’s high-value NFTs were securely sequestered within a cold storage hardware wallet, a cryptographic setup that requires physical interaction to sign transactions and transfer assets. Recognizing the active breach of his workstation, Crumz immediately terminated the computer’s power supply and severed internet connectivity to block any residual remote access channels.
Reflecting on the near-miss, Crumz issued a public warning to the broader crypto community via social media, emphasizing the stealthy nature of modern cyber attacks. Security analysts reviewing the incident noted that while the hardware wallet protected the core assets from direct extraction, the attackers likely aimed to compromise hot wallets, session keys, or underlying permissions associated with the victim’s broader Web3 activity.
The Broader Context: Social Engineering in the Web3 Era
The incident involving Crumz is not an isolated occurrence but rather part of a broader, systemic campaign targeting prominent figures within the digital asset ecosystem. Cybersecurity researchers specializing in blockchain forensics have observed a sharp pivot away from traditional smart contract exploits toward targeted social engineering.
Because prominent NFT collections like BAYC, CryptoPunks, and Azuki are associated with high-net-worth individuals, malicious actors frequently invest significant time and resources into reconnaissance. By posing as journalists, venture capitalists, conference organizers, or potential buyers, scammers build rapport over weeks or months. This patient approach allows them to bypass the instinctive skepticism that greets unsolicited links or direct messages, exploiting human vanity, professional ambition, or simple curiosity.
Industry experts emphasize that mainstream media outlets rarely, if ever, require third-party software installations, complex screen-sharing setups, or remote-control permissions simply to conduct an interview. Security protocols standard in traditional journalism rely on standard communication channels and verifiable corporate email domains, rather than anonymous social media direct messages.
Market Dynamics: BAYC Faces Declining Volume and Liquidity Pressures
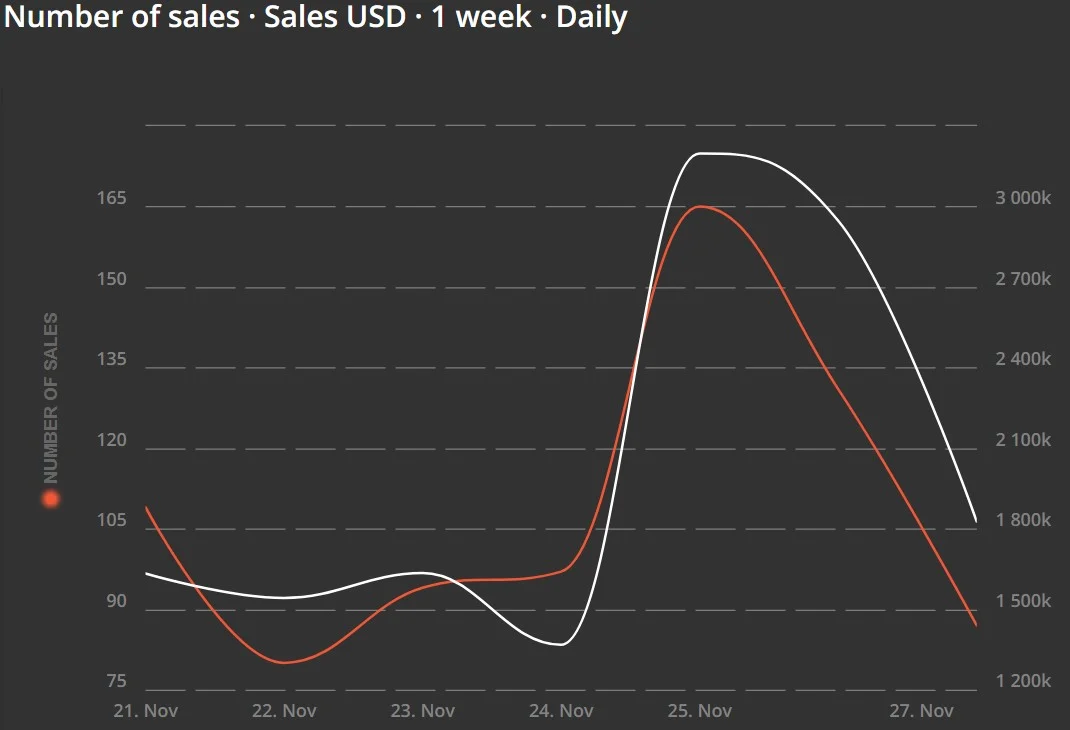
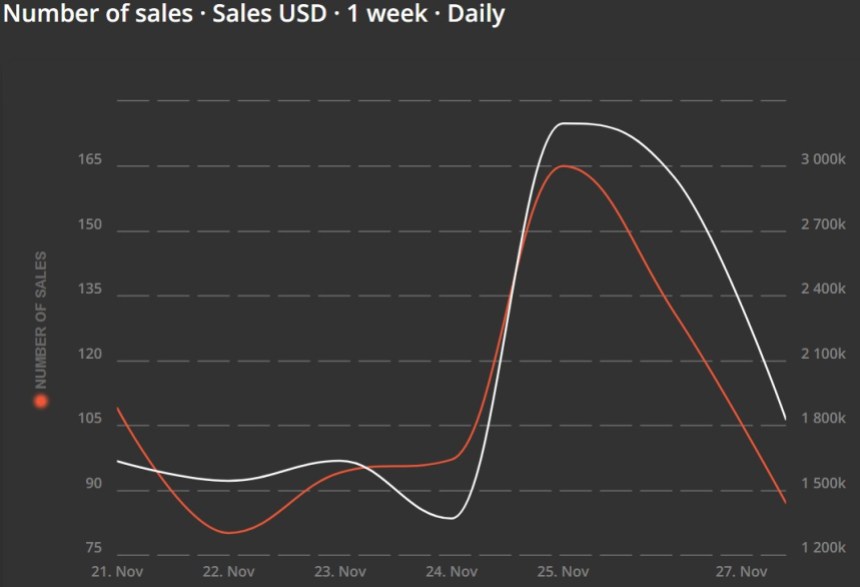
The security scare experienced by the BAYC collector unfolds against a challenging macroeconomic and structural backdrop for the broader Yuga Labs ecosystem and the NFT market at large. Recent market data from leading NFT trackers reveals a pronounced contraction in trading volume, liquidity, and primary sales metrics for the premier collection.
According to on-chain analytics, the frequency of BAYC transactions has experienced double-digit declines. Daily sales figures have dropped significantly from previous weeks, reflecting a broader cooling off in speculative retail interest across the digital collectible sector. Correspondingly, total sales volume denominated in U.S. dollars has contracted sharply, shedding millions of dollars in daily turnover compared to historical averages.
Primary sales metrics have similarly stagnated, registering periods of zero activity as primary minting events give way to secondary market price discovery. Secondary market liquidity—traditionally the lifeblood of blue-chip NFT projects—has also faced downward pressure, with floor prices experiencing volatility amidst shifting market sentiment and broader macroeconomic headwinds facing speculative crypto assets.
The contraction in trading volume extends to ApeCoin (APE), the native governance and utility token associated with the Bored Ape Yacht Club ecosystem. The token has faced sustained downward pressure on daily trading charts, reflecting a combination of risk-off sentiment among crypto investors, waning utility utilization, and broader liquidity drainage from altcoin markets. Analysts monitoring APE’s price action note that technical support levels have been tested repeatedly, underscoring the correlation between the health of the underlying NFT collections and the performance of their associated ecosystem tokens.
Implications for Digital Asset Collectors and Investors
The intersection of sophisticated social engineering attacks and contracting market liquidity highlights the multifaceted risks confronting participants in the digital asset space. While market downturns naturally test the financial resilience of investors, security breaches threaten their absolute capital preservation.
Security professionals recommend several foundational practices to mitigate the risks posed by social engineering campaigns:
- Verification of Identity: Always verify the credentials of individuals claiming to represent media outlets, investment funds, or corporate entities through official, independent communication channels (such as corporate email domains or official website contact pages).
- Separation of Duties: Never use a primary workstation containing active Web3 wallets, private keys, or seed phrases for general browsing, video conferencing, or interaction with unverified links and software.
- Hardware Isolation: Ensure that high-value digital assets remain locked behind air-gapped cold storage hardware wallets that cannot be accessed remotely via software vulnerabilities or browser compromises.
- Zero Trust Architecture: Adopt a strict zero-trust mindset regarding unexpected requests for remote access, screen sharing, or signature approvals, regardless of the perceived prestige or authority of the counterparty.
As the digital asset industry continues to mature, the tactics employed by malicious actors will likely continue to increase in psychological complexity. Incidents such as the attempted compromise of the BAYC collector serve as a stark reminder that in the decentralized finance and NFT sectors, vigilance remains the ultimate line of defense against capital loss.